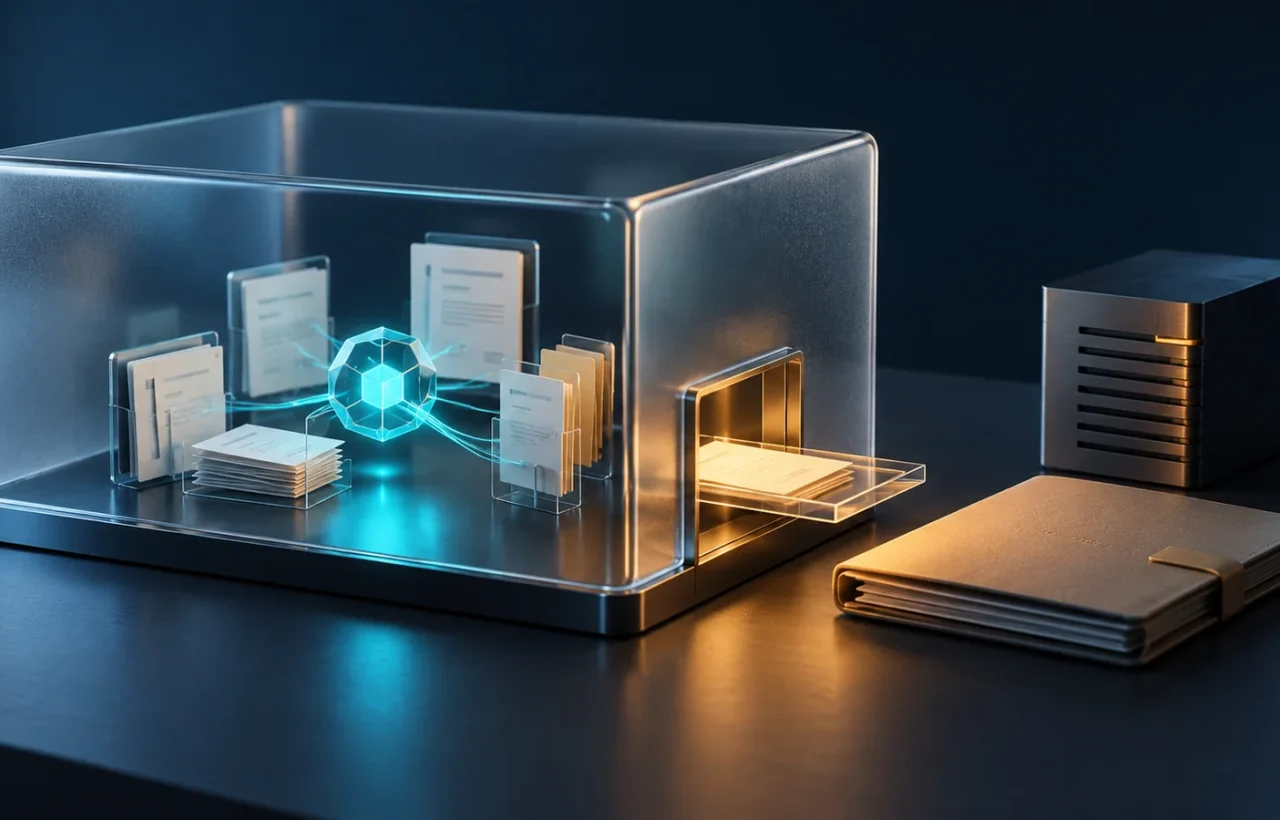
On September 28, NVIDIA announced Open Agent Safety Platform to control AI agents from testing through deployment. Its main elements are the OpenShell software runtime and a reference hardware architecture with Sentry. The announcement concerns systems where AI can access files, services and actions.
The boundaries OpenShell enforces
According to the OpenShell documentation, operators define permitted file paths, network connections and process restrictions. An agent works in an isolated environment. Network rules can allow only approved destinations, while filesystem rules keep unrelated directories outside the task’s reach.
In NVIDIA’s technical description, controls sit outside the agent itself: a separate Supervisor checks outbound requests, while the Sandbox restricts the working environment. Real credentials stay outside the agent workload and are attached to authorized requests. This makes permissions enforceable beyond a written instruction such as “leave other files alone.”
Imagine an assistant preparing a report from a copy of a spreadsheet. A sensible boundary would allow it to read that copy and write the result to a separate folder. Access to every company document or permission to delete originals is unnecessary. This is our example of defining a task, not a finding from testing OpenShell.
What Sentry adds
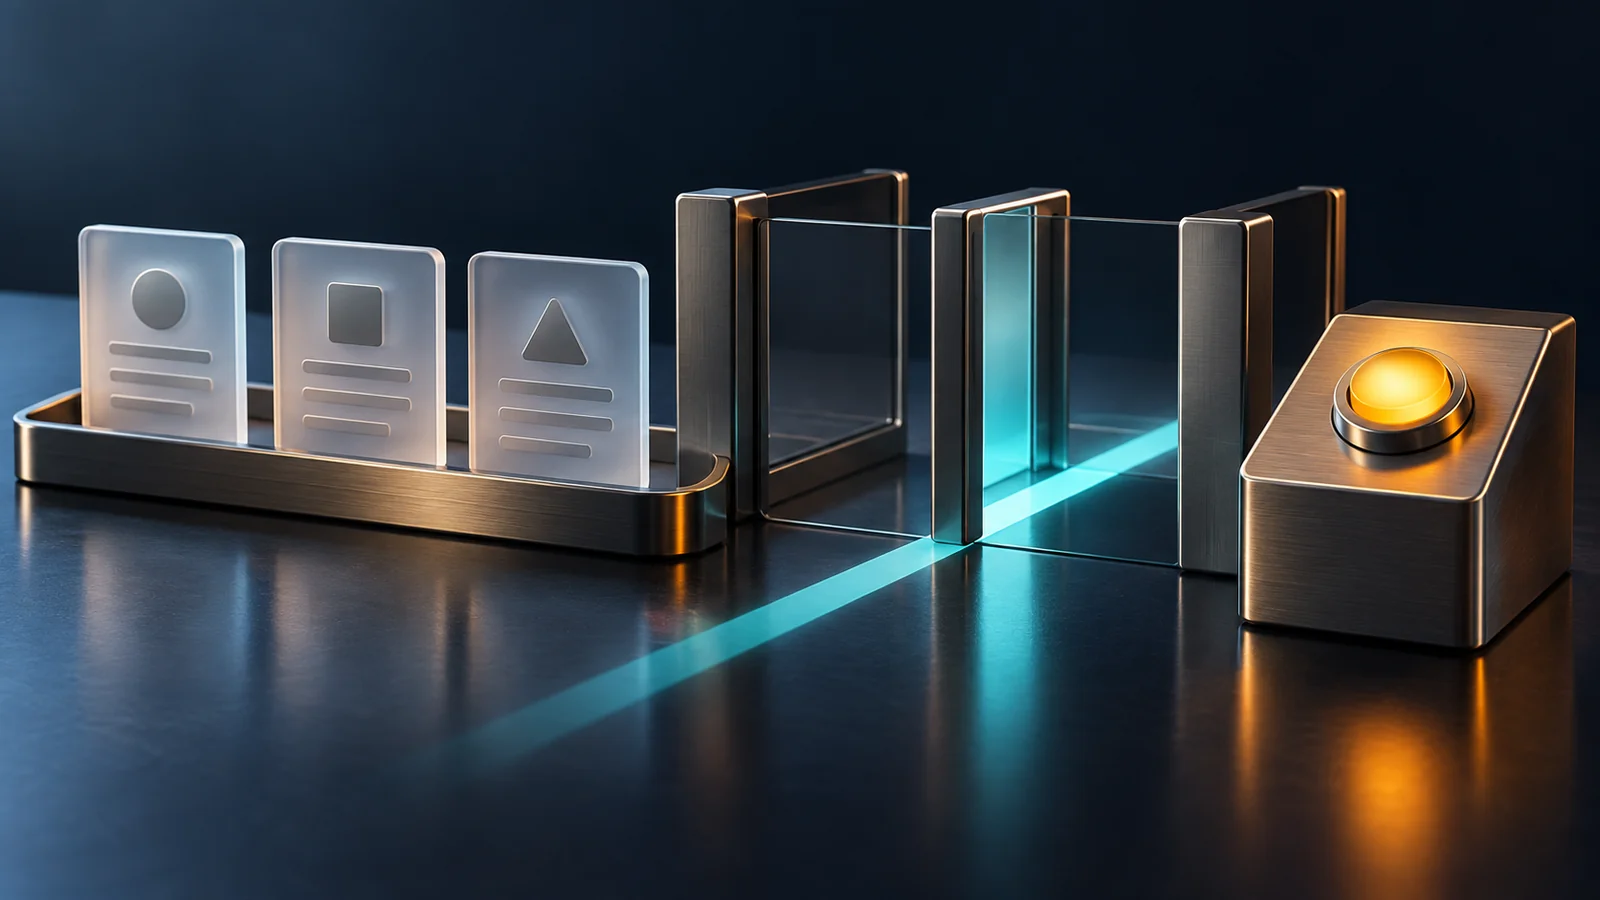
The reference architecture description places independent monitoring on BlueField-4 data processing units. In that configuration, Sentry observes activity and enforces policies outside the agent’s environment. NVIDIA describes it as an additional layer alongside OpenShell; downloading open-source code does not itself give a computer these hardware capabilities.
When evaluating the system, establish which configuration is actually deployed: software isolation alone or hardware enforcement as well. The platform name does not fully describe the protection in a particular installation.
What is available to examine
The OpenShell code is on GitHub under Apache 2.0. Its repository documentation supports local use on Linux or Apple Silicon Macs; Windows through WSL 2 is marked experimental. Policy changes undergo formal checks for risky expansion of access, which is intended to wait for human review.
This is a tool for people running and administering agents. If you use a finished service instead, useful questions for its provider include:
- Exactly which data and external services can the assistant reach?
- Who can expand its permissions, and where can activity logs be reviewed?
- How can execution be stopped and data recovered after a mistake?
Our conclusion: access controls constrain possible actions, but do not themselves verify that a report is factual or its conclusion correct. The result needs a separate check. If you use ready-made integrations instead of running your own agent, see our explanation of ChatGPT Voice plugin permissions as well.

Join the conversation
Stay on topic and respect other readers. Your first comment may appear after editorial review.